AI 應用 · IT 委外 · 資安檢測 Enterprise AI · Managed IT · Security Testing

協助企業落實
AI 應用與資訊安全

Putting Enterprise AI and Information Security into Practice

椰林科技提供企業 AI 智慧化應用服務、ISO/IEC 27001 合規 IT 委外服務,以及滲透測試與 APP 資安檢測,針對客戶實際遇到的問題量身打造解決方案,從規劃、導入到驗證,建立可持續的資安管理。

COCO TECHS provides enterprise AI application services, ISO/IEC 27001-compliant managed IT services, penetration testing and app security testing — tailored to the problems each client actually faces, from planning through deployment and verification.

服務項目

Our Services

以顧問與委外服務協助建立並維運資安制度,並以滲透測試與 APP 資安檢測驗證實際防護成效。

Consulting and managed services to build and run your security program, and testing to verify how well your defenses actually hold up.

AI 方案AI Solutions

企業 AI 智慧化應用服務

Enterprise AI Application Services

針對客戶實際遇到的問題,量身打造 AI 解決方案——從需求訪談與資料盤點、概念驗證(PoC),到系統整合、上線與持續優化,讓 AI 真正解決營運上的問題。

AI solutions built around the problem each client actually faces — from requirements and data review through a proof of concept to integration, go-live and continuous improvement.

  • 需求訪談與可行性評估Requirements & feasibility assessment
  • 概念驗證(PoC)與方案設計Proof of concept & solution design
  • 系統整合、上線與持續優化Integration, go-live & continuous improvement
參考成功案例 →See case studies →
委外服務Managed Services

ISO/IEC 27001 合規 IT 委外服務

ISO/IEC 27001-Compliant Managed IT Services

以符合 ISO/IEC 27001 要求的作業程序承接您的 IT 維運,從系統、網路到帳號權限與備份管理,每項作業皆留存紀錄、可供稽核,讓委外同時滿足日常營運與資安合規。

We run your IT operations under procedures that meet ISO/IEC 27001 requirements — systems, networks, access and backups — with every task recorded and audit-ready, so outsourcing serves both day-to-day operations and security compliance.

  • 系統、網路與端點日常維運Day-to-day system, network & endpoint operations
  • 帳號權限、備份還原與修補管理Access, backup/restore & patch management
  • 作業紀錄依 ISO/IEC 27001 留存,隨時可供稽核Records kept to ISO/IEC 27001, audit-ready at any time
檢測服務Testing

滲透測試

Penetration Testing

針對網路、應用系統與生成式 AI 應用進行滲透測試。採兩階段執行:先以 AI 輔助的自動化工具收斂測試範圍,再由具 OSCP / CEH 認證的測試人員針對高風險路徑進行人工驗證。

Penetration testing of networks, applications and generative-AI systems, in two stages: AI-assisted automated tooling narrows the scope, then OSCP / CEH-certified testers manually verify the high-risk attack paths.

  • 傳統:網路 / Web / API / AD / 雲端Traditional: network / web / API / AD / cloud
  • AI 應用:提示注入、資料投毒等AI apps: prompt injection, data poisoning
  • CVSS 風險評級與修補後複測CVSS ratings & post-fix retest
查看測試流程 →See our process →
檢測服務Testing

APP 資安檢測

App Security Testing

對齊「行動應用 App 基本資安檢測基準 V4.3」執行行動應用程式資安檢測,涵蓋五大檢測構面與 L1–L3+F 分級,逐項提供檢測結果與佐證,並提出修補建議。

Mobile-app security testing aligned with Taiwan's Mobile App Basic Security Testing Baseline V4.3 — five testing dimensions and Levels L1–L3 + F, with per-item results, evidence and remediation advice.

  • 五大構面;L1 25 · L2 31 · L3 39 · F 9 項Five dimensions; L1 25 · L2 31 · L3 39 · F 9 items
  • 逐項通過/未通過+佐證Per-item pass/fail with evidence
  • 適用政府與高信任部署For government & high-trust deployments

滲透測試流程

Penetration-Testing Process

先以自動化工具完成偵察與弱點對應,再由測試人員進行人工滲透與驗證,降低誤報,並找出自動化工具難以發現的問題。

Automated tooling handles reconnaissance and vulnerability mapping; testers then perform manual exploitation and verification — reducing false positives and finding issues automated tools miss.

  1. 1偵察Recon
  2. 2掃描Scanning
  3. 3弱點對應Vuln Mapping
  4. 4漏洞利用Exploitation
  5. 5深入滲透Penetration
  6. 6後滲透Post-Exploitation
第一階段 · 步驟 1–4Stage 1 · Steps 1–4

AI 輔助自動化測試

AI-Assisted Automated Testing

  • 快速偵察與服務 / 連接埠辨識Rapid recon & service / port identification
  • CVE 對應與可利用性評分CVE mapping & exploitability scoring
  • 收斂測試範圍,排定人工測試優先順序Narrows scope and prioritizes manual testing
第二階段 · 步驟 5–6Stage 2 · Steps 5–6

人工滲透測試

Manual Penetration Testing

  • 針對高風險路徑進行人工滲透Manual exploitation of high-risk paths
  • 橫向移動與權限提升Lateral movement & privilege escalation
  • 驗證可利用性並排除誤報Confirms exploitability and rules out false positives

交付內容:完整發現報告與概念驗證(PoC)、每項弱點 CVSS 風險評級、優先排序修補路線圖、修補後複測與驗證。 Deliverables: detailed findings report with proof-of-concept, CVSS risk rating per finding, prioritized remediation roadmap, and post-fix retest & verification.

關於我們

About Us

椰林科技(COCO TECHS)位於台北,提供資安顧問、IT 委外與資安檢測服務,服務對象包括政府機關、金融、電信與科技產業。我們協助客戶將資安與 AI 治理要求,轉化為可執行的制度、技術控制與持續改善。

Based in Taipei, COCO TECHS provides cybersecurity consulting, managed IT and security testing to government agencies and the finance, telecom and technology sectors. We help clients turn security and AI-governance requirements into workable policies, technical controls and continual improvement.

資安顧問Cybersecurity Advisory

  • 勒索病毒防禦Ransomware defense
  • 雲端資安Cloud security
  • 零信任架構Zero Trust architecture
  • 5G / MEC 資安5G / MEC security
  • OT / 工控資安OT / industrial security
  • 可信任 AITrustworthy AI

AI 與技術導入AI & Technology Adoption

  • AI 資安分析AI security analytics
  • AI 流量偵測AI traffic detection
  • 加密流量分析Encrypted-traffic analysis
  • 5G 威脅防禦5G threat defense
  • 知識圖譜問答Knowledge-graph Q&A
  • AI 應用部署AI application deployment

專業證照Certifications

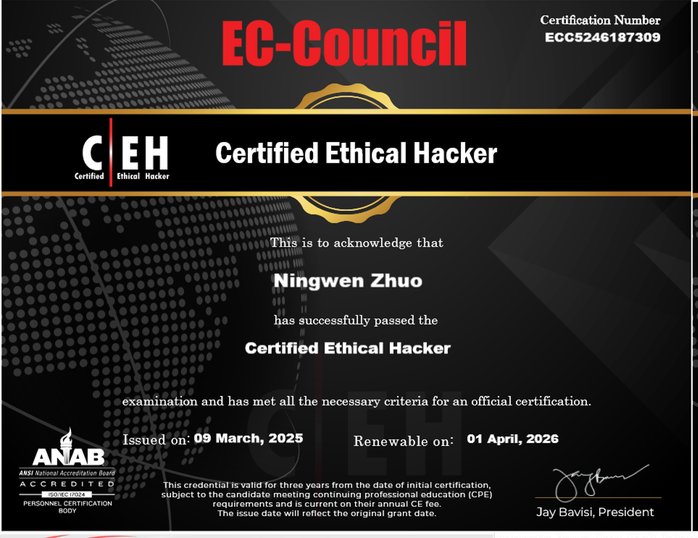
團隊成員持有之國際認證與訓練證書,點選可檢視原圖。International certifications and training certificates held by our team. Select one to view the original.

  • CEH 道德駭客認證證書(EC-Council)

    CEH 道德駭客認證Certified Ethical Hacker (CEH)

    EC-CouncilEC-Council

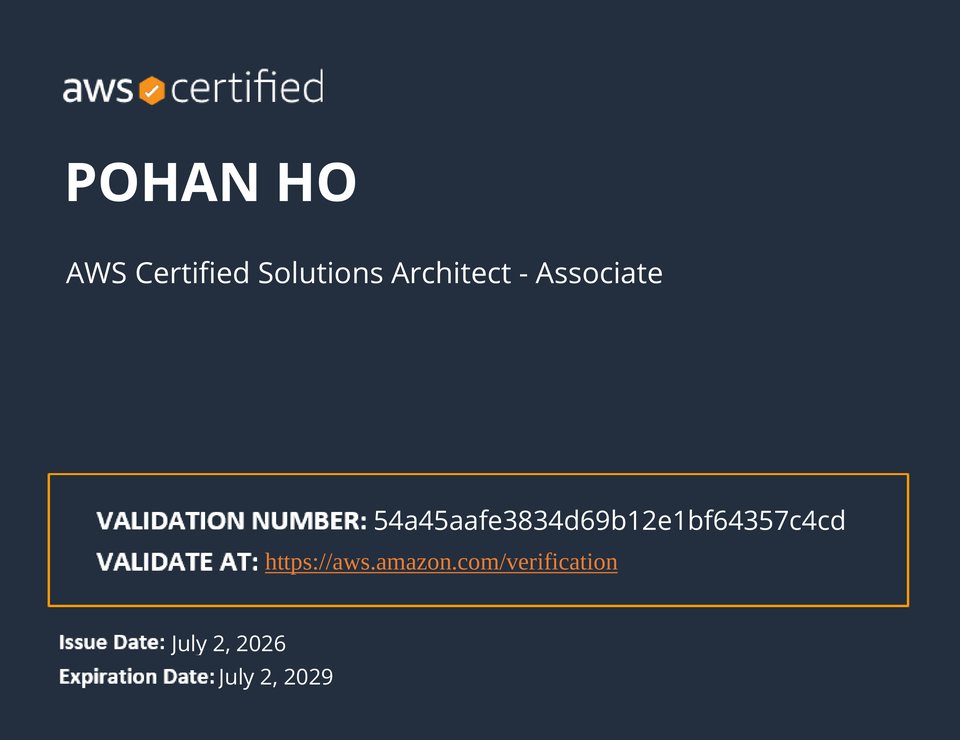
  • AWS Certified Solutions Architect – Associate 證書(Amazon Web Services)

    AWS 解決方案架構師(Associate)AWS Certified Solutions Architect – Associate

    Amazon Web Services(AWS)Amazon Web Services (AWS)

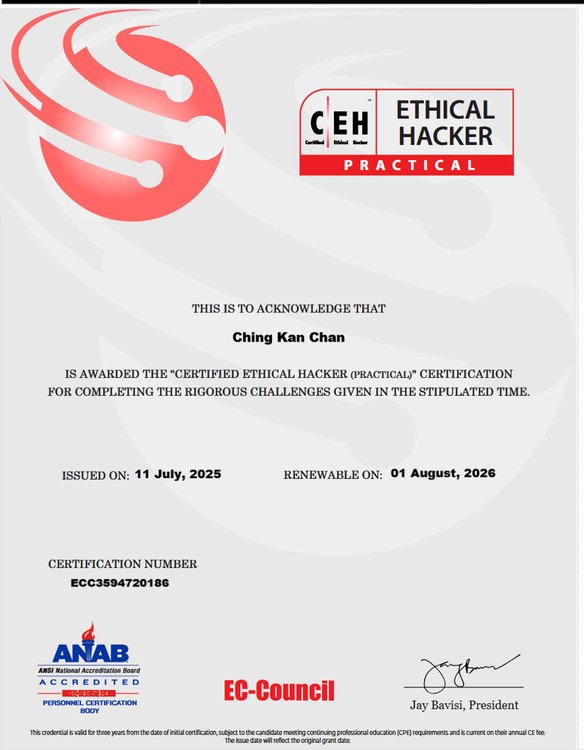
  • CEH Practical 實作認證證書(EC-Council)

    CEH Practical 實作認證Certified Ethical Hacker (Practical)

    EC-CouncilEC-Council

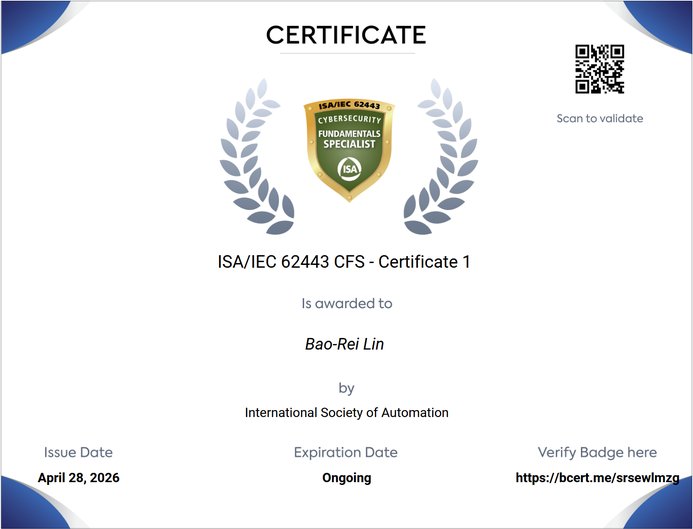
  • ISA/IEC 62443 資安基礎專家(CFS)證書(國際自動化學會(ISA))

    ISA/IEC 62443 資安基礎專家(CFS)ISA/IEC 62443 Cybersecurity Fundamentals Specialist

    國際自動化學會(ISA)International Society of Automation (ISA)

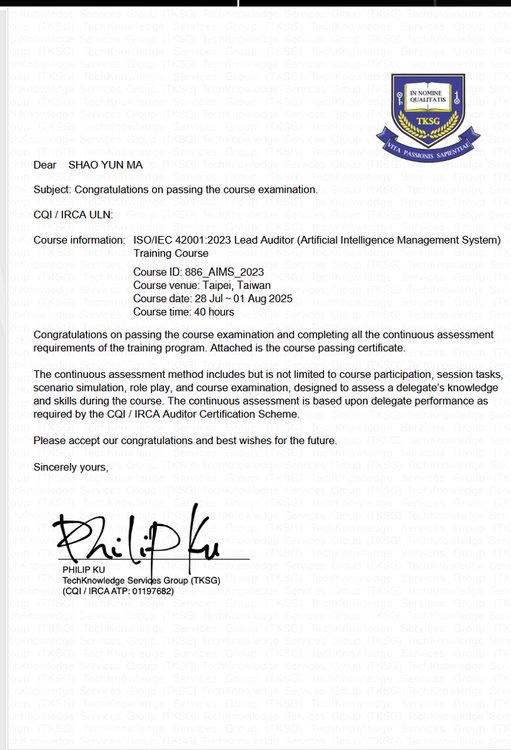
  • ISO/IEC 42001:2023 主導稽核員課程合格證書(CQI / IRCA 認可課程(TKSG))

    ISO/IEC 42001:2023 主導稽核員課程合格ISO/IEC 42001:2023 Lead Auditor course — passed

    CQI / IRCA 認可課程(TKSG)CQI / IRCA-certified course (TKSG)

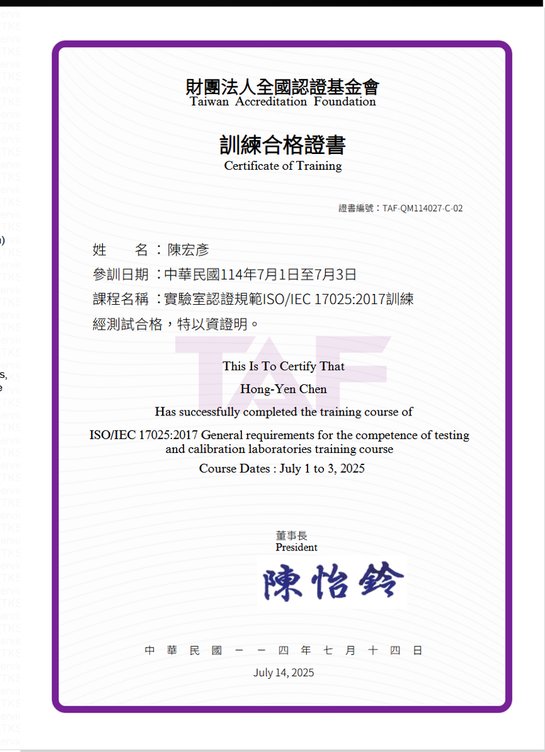
  • ISO/IEC 17025:2017 訓練合格證書證書(財團法人全國認證基金會(TAF))

    ISO/IEC 17025:2017 訓練合格證書ISO/IEC 17025:2017 training certificate

    財團法人全國認證基金會(TAF)Taiwan Accreditation Foundation (TAF)

聯絡我們

Contact Us

想了解企業 AI 應用、IT 委外服務,或滲透測試、APP 資安檢測?歡迎填寫表單或來信,顧問將與您確認需求範圍,並提供初步建議與報價。

Interested in enterprise AI applications, managed IT services, penetration testing, or app security testing? Send us the form or email us — a consultant will confirm the scope with you and follow up with initial recommendations and a quote.

如需現場簡報或長期顧問合作,請一併留下單位名稱與可聯絡時段。我們將於 1–2 個工作天內回覆。

For an on-site briefing or long-term advisory engagement, please include your organization and preferred contact times. We reply within 1–2 business days.

我們重視您的隱私,所有資料僅供諮詢聯繫使用。We respect your privacy; your information is used only to respond to your inquiry.

感謝您的諮詢!Thank you!

我們將於 1–2 個工作天內回覆您,請留意您的信箱。We'll reply within 1–2 business days. Please watch your inbox.